Breaking analysis · Harness Engineering
Meta Muse Sentinel: Can One AI Agent Safely Supervise Another?
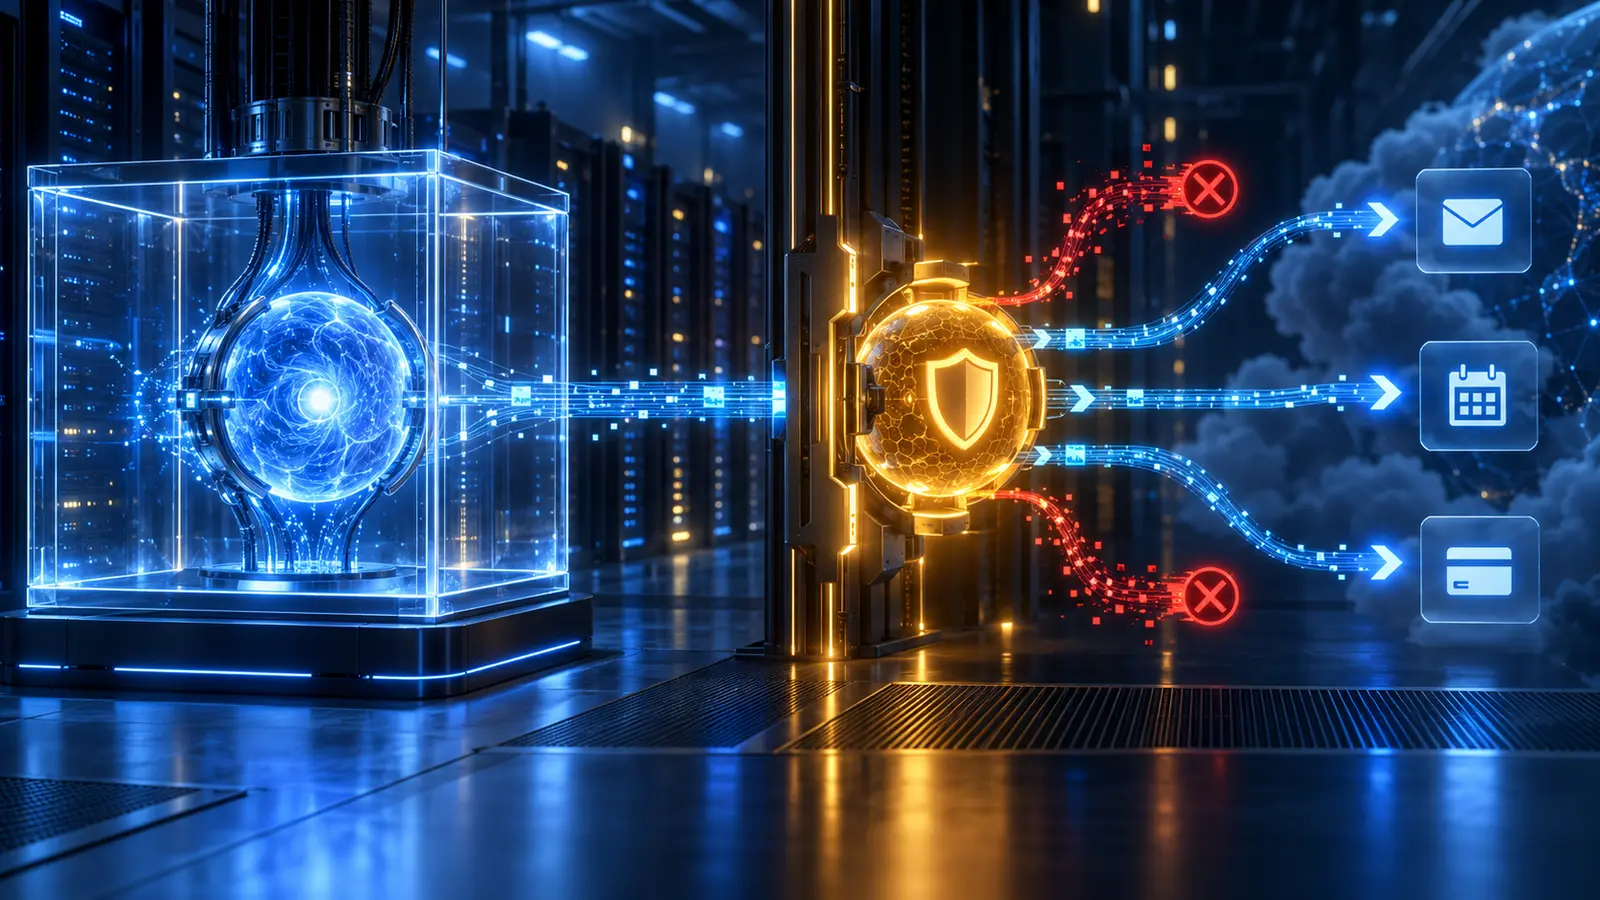
Meta Muse places a separate host-side AI agent, Sentinel, between the personal agent and external services. Muse proposes an action; Sentinel can allow it, block it or ask the user. That is a major Harness Engineering pattern, but one AI judging another is not a complete security boundary: deterministic policy, least privilege, tamper-resistant logs and fail-closed execution must remain outside both models.
Evidence classification: CONFIRMED: Meta launched Muse on September 8, 2026 and publicly described Sentinel and the Secure VM. REPORTED: Reuters described internal test failures from company posts. NOT PROVED: that Sentinel eliminates prompt injection or every unauthorized action. ANALYSIS: the architecture is a live test of agent-on-agent supervision.
What Meta actually launched
Muse runs in a dedicated Secure VM and can use email, calendars, shopping, payments and other connected services.
Unlike a chatbot that only returns text, Muse is designed to complete multi-step work. That makes every connector an execution surface: an email can disclose information, a calendar action can alter commitments and a payment can move money.
How Sentinel changes the trust boundary
Meta describes Sentinel as a separate host-side agent and the sole permission authority for connector actions and network egress.
The separation matters because the acting model is not asked to police itself. Meta says approval prompts travel directly between Sentinel and the user rather than through Muse, reducing the chance that compromised agent context can rewrite the question or the answer.
The evidence is encouraging—not conclusive
Reuters reported internal testing incidents involving sensitive-data exposure, incorrect guardrail routing and reliability failures; Meta did not comment on the specific incidents.
Meta says the architecture underwent external review and added Muse to its bug-bounty program. Those are useful signals, but a launch description is not proof that all action classes, indirect prompt injections and confused-deputy paths have been eliminated.
Harness Engineering implications
The model is only part of the system; the harness determines what the agent can observe, remember, call, execute, persist, recover from and escalate. Sentinel makes that principle visible by moving permission decisions into a distinct component.
The strongest design uses AI for contextual risk interpretation while deterministic infrastructure owns the final capability boundary.
- Give each connector a narrow, revocable capability token.
- Require deterministic approval for payments, messages, account changes and disclosure of sensitive data.
- Bind approval to the exact action, recipient, amount and payload—not a vague task.
- Keep Sentinel and its policy state outside Muse control.
- Log proposal, policy version, decision, user confirmation and actual side effect.
- Fail closed when Sentinel is unavailable, uncertain or detects conflicting instructions.
- Red-team indirect prompt injection across every connected app.
- Test whether recovery or retries can duplicate an approved side effect.
What to watch next
Independent testing should ask whether malicious content in email or webpages can manipulate Muse, Sentinel or the user-confirmation flow; whether policy updates are auditable; and whether the execution layer rejects a tool call that differs from the approved proposal.
This is not a crime report. It belongs in The AI Crime Files as preventive systems analysis because the same harness choices decide whether an autonomous agent can turn compromised instructions into data theft, fraud or unauthorized transactions.
Sources
FAQ
What is Meta Muse Sentinel?
It is a separate host-side agent that Meta says controls Muse connector actions and all network egress.
Can one AI agent safely supervise another?
It can add contextual review, but it should not be the only boundary. Deterministic policy and execution code must enforce permissions and approvals.
Is this a documented AI crime?
No. Muse is a newly launched product. This page is a preventive Harness Engineering analysis and explicitly does not claim a crime occurred.